Regulatory and compliance context
Financial institutions carry PDPA obligations plus sector-specific regulatory expectations around data security, uptime and audit trails. Network segmentation, documented change management and a defensible security posture aren't optional here — they're what a regulator or auditor will ask to see first.
Financial institutions run on infrastructure that has to satisfy both operational reliability and a regulator’s expectations — network segmentation, documented change management, and a security posture that holds up under audit.
What financial institutions need from IT
Structured cabling and network infrastructure built to a documented standard, cybersecurity controls that satisfy both operational needs and audit expectations, and independent assessment support when a regulator or internal audit asks for it.
Common problems we’re called in to fix
Network infrastructure installed without documentation an auditor can review, security controls that were adequate at a smaller scale but haven’t been reassessed, and no independent audit trail for infrastructure changes.
How we work with finance clients
Engagements typically combine structured cabling and network infrastructure work with cybersecurity controls from day one, documented to a standard that holds up under later audit or regulatory review.
Services most relevant to you
Surveyed in this sector
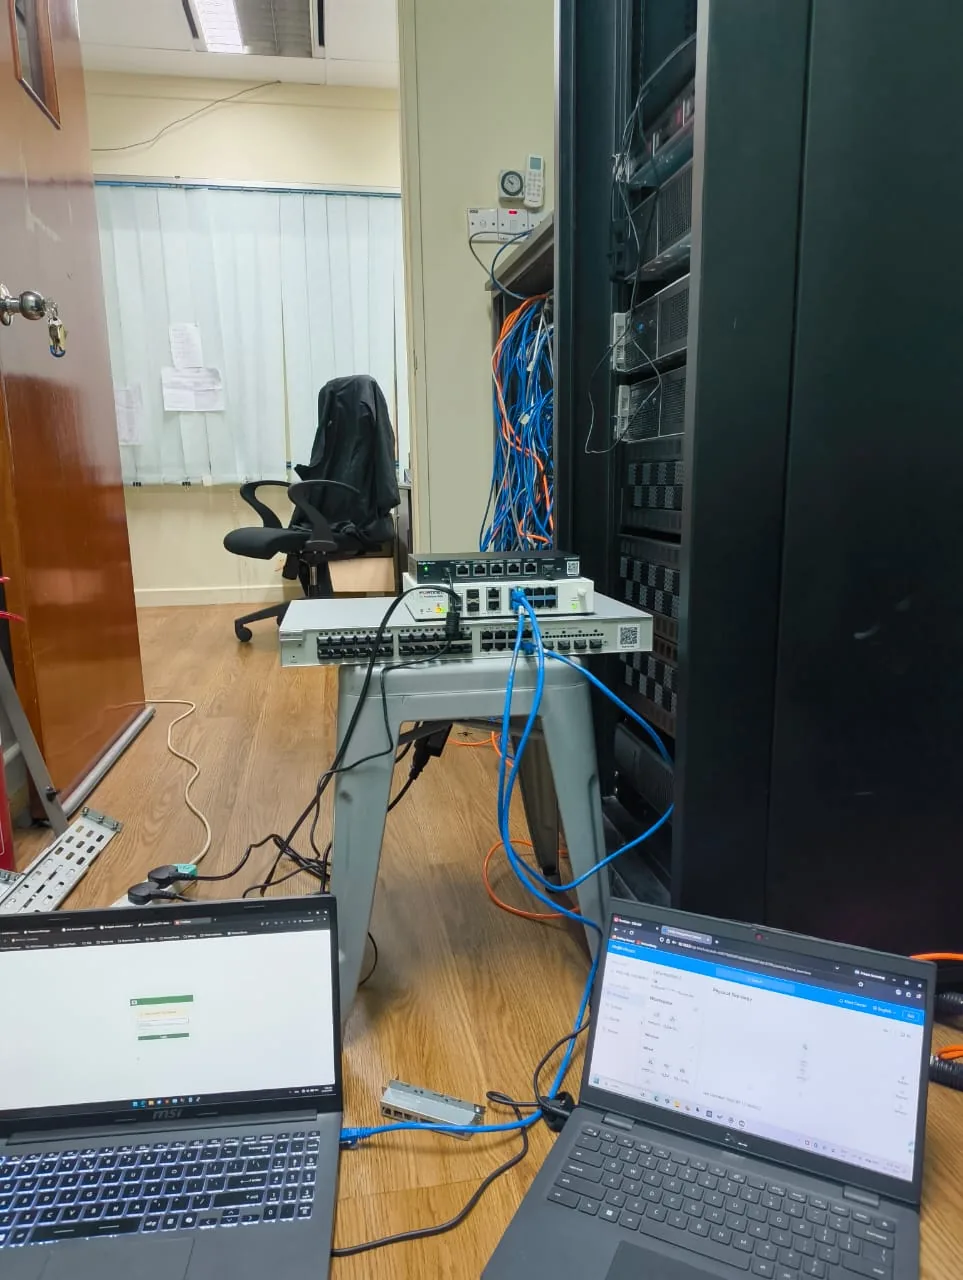
FortiGate firewall migration for a Sabah financial GLC
FortiGate 60F-to-90G firewall migration and multi-WAN network upgrade for a Sabah government-linked financial company, delivered in one day after a week of network study.
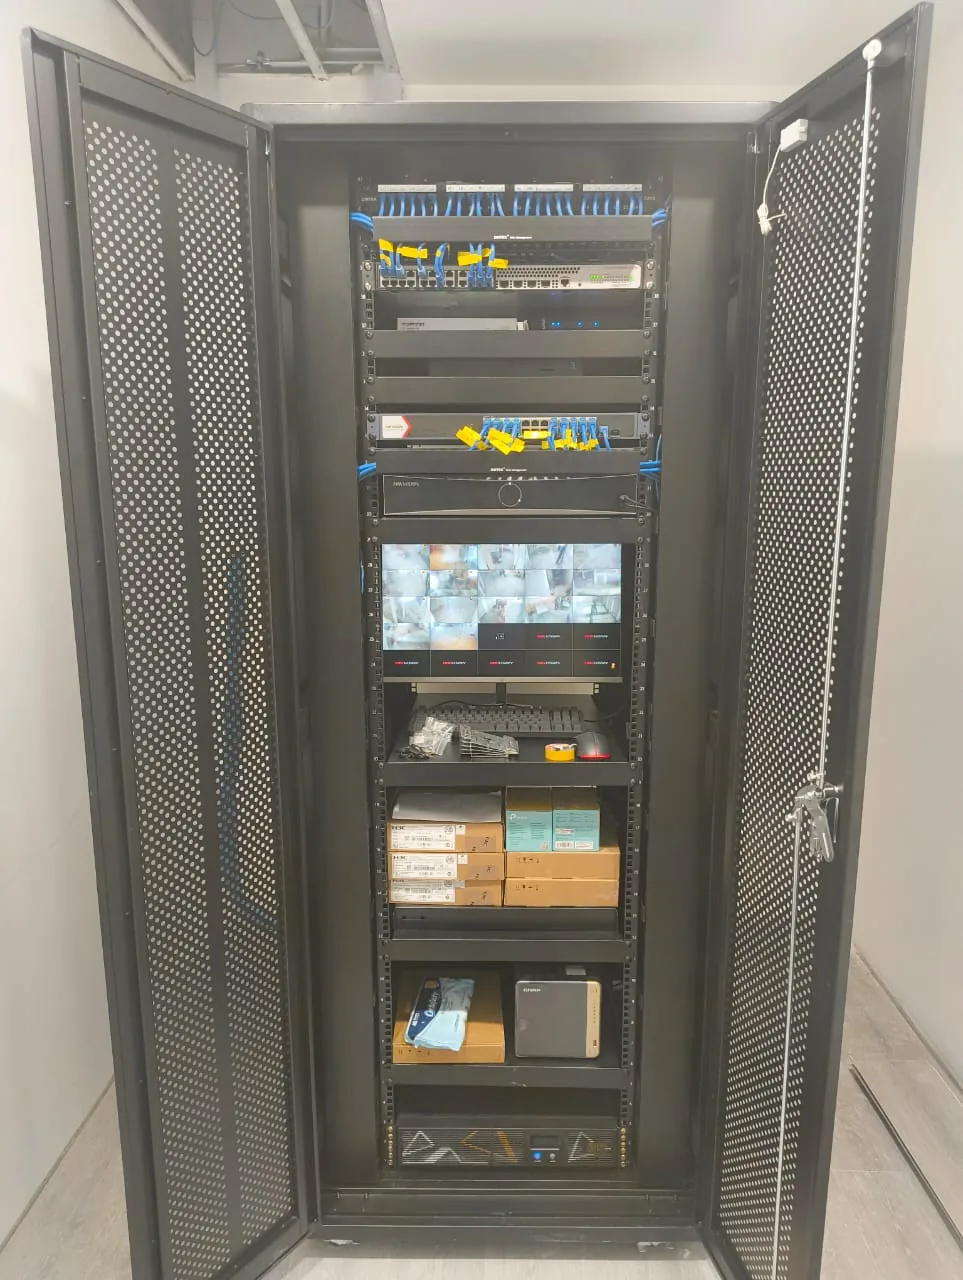
Full IT infrastructure and structured cabling build for a Japanese investment bank in Labuan
A full IT infrastructure build for a Japanese investment bank's Labuan branch — network design, AP heatmap analysis, CCTV placement, and structured cabling delivered end-to-end in two months.